PicoCTF JAuth Walkthrough
April 03 2024 - 2 Minutes
picoctf - walkthrough
This is a difficult challenge! Be warned!
Hello again! Welcome back for another picoctf walkthrough.
Today I am going to walkthrough JAuth, which with just over 2000 solves on picoctf, is one of the hardest web explotation challenges in picoctf.
Starting
We are given a link to a website, clicking on the link we see this:
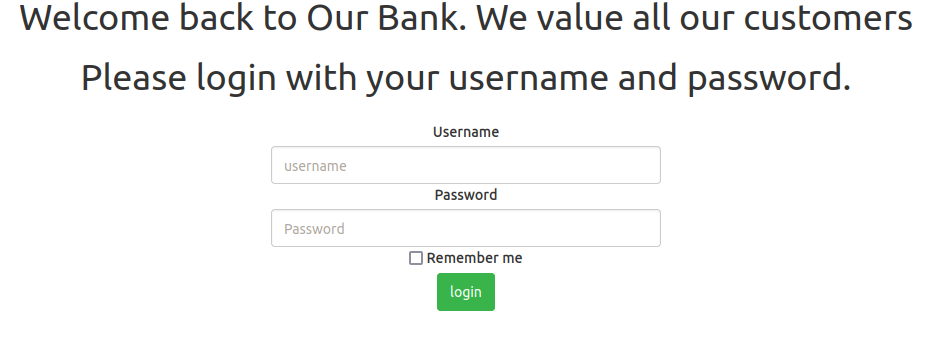
Logging in with the given username and password, test and Test123!, gets us to this screen:
This is kind of boring, lets look at the cookies!
There are the two cookies from the website:
- PHPSESSID - v70vqqvvcgp6v52gm51o97qllv
- token - eyJ0eXAiOiJKV1QiLCJhbGciOiJIUzI1NiJ9.eyJhdXRoIjoxNzEyMTYwMTU3MzQ5LCJhZ2VudCI6Ik1vemlsbGEvNS4wIChYMTE7IFVidW50dTsgTGludXggeDg2XzY0OyBydjoxMjMuMCkgR2Vja28vMjAxMDAxMDEgRmlyZWZveC8xMjMuMCIsInJvbGUiOiJ1c2VyIiwiaWF0IjoxNzEyMTYwMTU3fQ.Vu7aAEVZUqaUIgqniogW0knqaxLf7JYy8wKvc53f3zk
That token cookies looks interesting, lets inspect it a bit more ...
The Plot Thickens
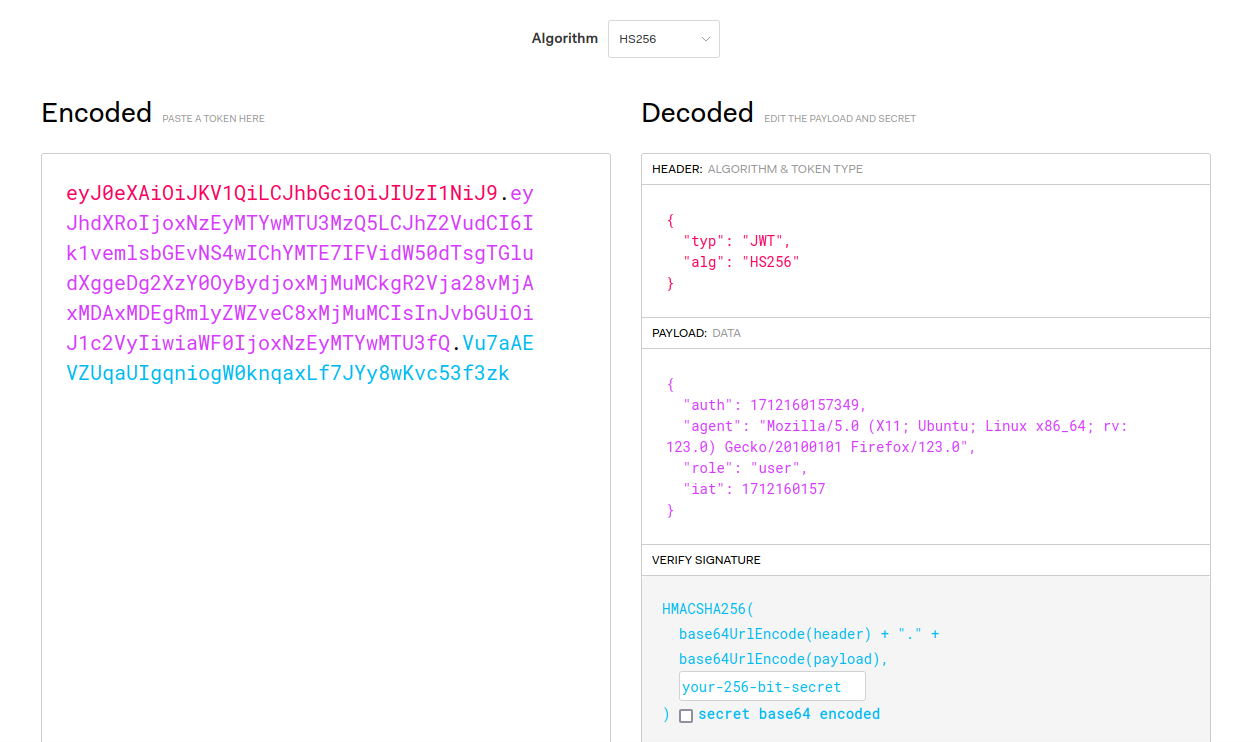
That token cookie has periods in it, two of them, which reminds me of a json web token.
To test this I used the site for json web tokens.
Putting the content of the cookie into the site, shows us this, confirming that it is in fact a JWT.
Some JWT libraries include two functions, verify and decode.
decode only decodes the content within the JWT, without verifing the signature.
Some developers assume that decode will also verify the JWT, this is the vulernability that we will exploit.
Exploitation
Using another JWT site, we can edit the content of the JWT, mostly this single line.
We change the line "role": "user" to "role": "admin".
Now that we have edited the token, we need to execute the vulernability. We run the JWT site without any algorithm.
This means that we can edit the token as much as we want, and the website will not know.
But, the new token only has one period, unlike the two in the original token, to fix this we just have to add a single period to the end of the new token.
Now replacing the cookies value on the website and reloading the page, brings us to this:
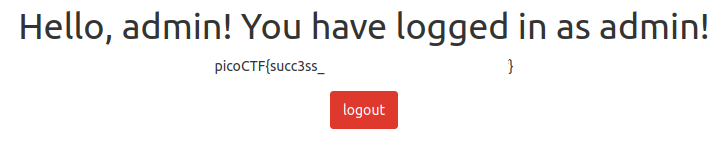
Success! we made it to the flag, now lets talk about mitigation.
Mitigation
Make sure that the JWT library actually verifies the JWT, if it does not do it automatically, DO IT YOURSELF!
Simply put, make sure that you actually verify the JWT.
Thank you for reading this post, I hope you have a nice day.